Bose Technology Solutions is built around a single data model so your risks, controls, evidence, vendors, policies, and incidents stay perfectly in sync — no more reconciling four different sources of truth.
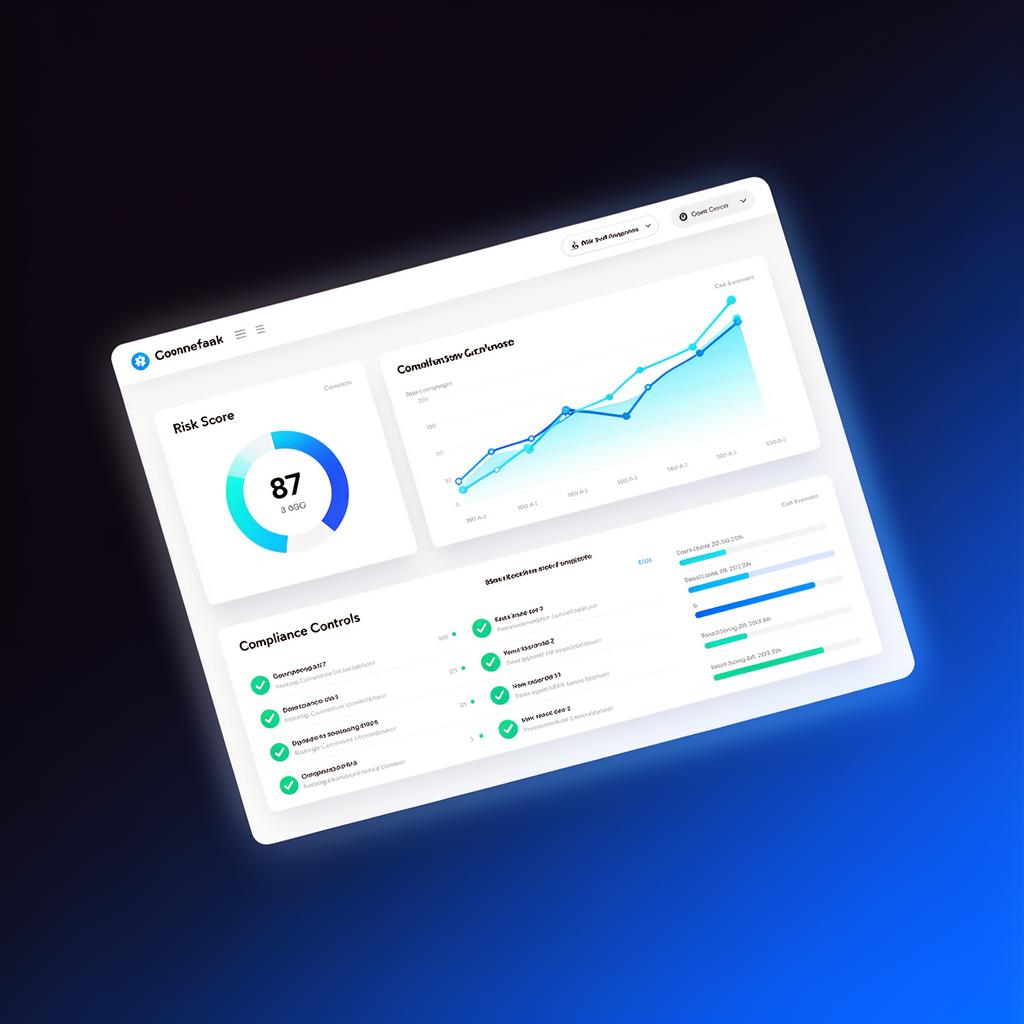
A shared object graph connects risks, controls, evidence, frameworks, vendors, policies, and incidents — automatically.
Quantitative & qualitative scoring with AI-assisted analysis.
Cross-walk controls across SOC 2, ISO 27001, NIST CSF, HIPAA, PCI, GDPR.
Continuous evidence collection, sampling, and reviewer workflows.
Inherent & residual scoring, contract reviews, continuous monitoring.
Lifecycle authoring, approvals, attestations, version history.
Playbooks, post-mortems, and automatic linkage to root-cause risks.
Our GRC co-pilot drafts policies, summarises evidence, recommends controls, and flags drift — so your team focuses on the decisions that matter.
Bose Technology Solutions runs on hardened cloud infrastructure with SOC 2 Type II, ISO 27001, and HIPAA-aligned controls. Your data is encrypted in transit and at rest, with optional customer-managed keys.
See how teams cut audit prep time by 60% and unify risk across the business with Bose Technology Solutions.